- Details
- 2026-10-12 10:26:04
Our Blog
Hackerstorm Makes Enriched CISA KEV Data Available via JSON and RSS
Hackerstorm Threat Intelligence
Audience: Vulnerability Managers, Security Operations, CISOs, DevSecOps Teams
Reading Time: Approximately 10 minutes
Subscribe to get these articles directly to your inbox when published
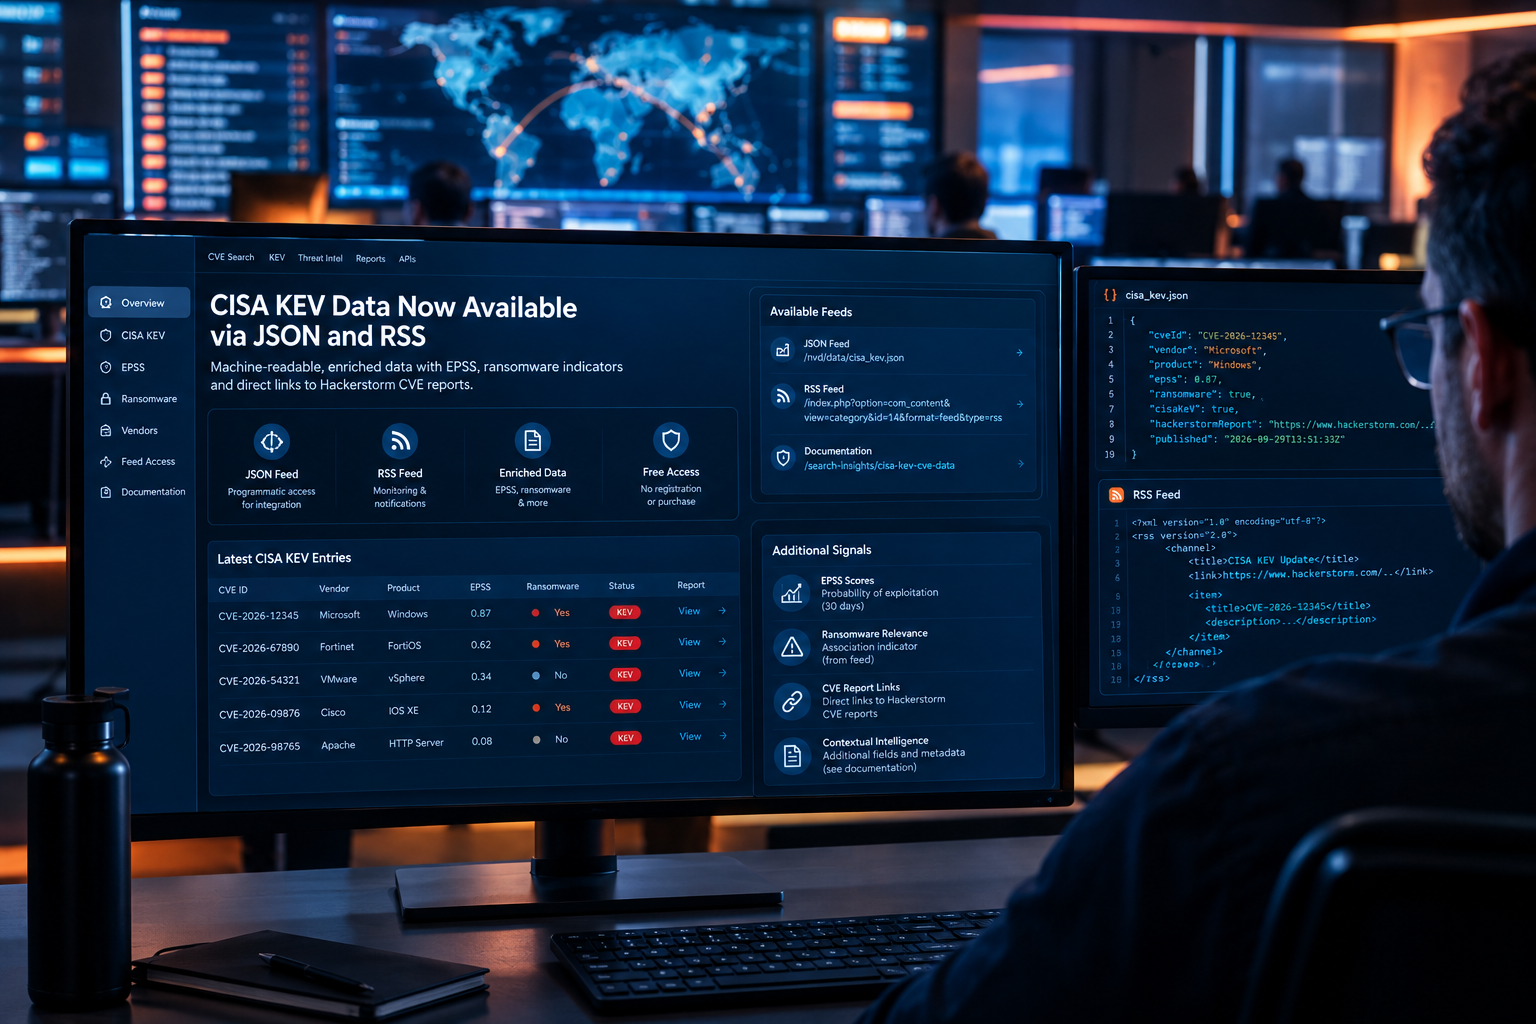
Hackerstorm has made free, machine-readable enriched data based on the CISA Known Exploited Vulnerabilities (KEV) Catalog available through public JSON and RSS feeds. Alongside KEV status, the feeds provide additional vulnerability signals, including EPSS scores, ransomware relevance indicators and direct links to Hackerstorm CVE reports. The data is accessible without registration or purchase and is intended for security operations teams, vulnerability managers, researchers, developers and security-tool integrators building their own workflows, dashboards and tooling.
Availability
♦ JSON feed: https://www.hackerstorm.com/nvd/data/cisa_kev.json
♦ RSS feed: https://www.hackerstorm.com/index.php?option=com_content&view=category&id=14&format=feed&type=rss
♦ Documentation and data access: https://www.hackerstorm.com/search-insights/cisa-kev-cve-data
The JSON feed is the primary structured data source for programmatic consumption and integration. The RSS feed supports feed-based monitoring and notification workflows.
What the Feeds Contain
The CISA Known Exploited Vulnerabilities (KEV) Catalog identifies vulnerabilities that have been exploited in the wild. The Hackerstorm feeds retain CISA KEV information and add further signals where available:
♦ EPSS scores and associated data, where available. EPSS is a probability estimate of exploitation in the wild over the next 30 days.
♦ Ransomware relevance indicators, as recorded in the feed. A flag reflects the association recorded for that vulnerability and does not indicate use in every ransomware campaign.
♦ Direct links to the corresponding Hackerstorm CVE report.
♦ Additional contextual vulnerability intelligence present in the published feed, with field information provided on the documentation page.
KEV inclusion reflects confirmed exploitation. EPSS is a predictive estimate and does not confirm exploitation or measure risk to a specific organisation.
Practical Applications
SOC and security operations teams: correlating KEV entries with other security data, with EPSS and ransomware context held in the same record.
Vulnerability management teams: supporting remediation prioritisation with confirmed exploitation, EPSS and ransomware indicators alongside each entry. Prioritisation decisions remain with the consuming team.
Security researchers: analysing vulnerability trends across vendors, products and time periods from structured data.
Developers and integrators: incorporating the JSON feed into dashboards, reporting, automation and custom security tooling, and using the RSS feed for monitoring in feed readers and notification pipelines.
Related articles
Ensure you understand the latest KEV additions to cover off any potential gaps in your remediation activities. View all weekly reports here
Further Reading
The following resources offer technical analysis to help integrate CISA KEV data into operational triage workflows and stay aligned with updated mitigation guidance.
Lookup scores, news, poc's, threat intel, vendor advisory status, and exploit vectors in real time.
hackerstorm Dynamic Intelligence
Need live data on specific KEVs from this roundup?
About Hackerstorm
Hackerstorm is a vulnerability intelligence platform providing CVE reports and enriched vulnerability data, including KEV status, EPSS and ransomware signals, for security practitioners, researchers and developers. Further information is available at www.hackerstorm.com.
Author Information
Timur Mehmet | Founder & Lead Editor
Timur is a veteran Information Security professional with a career spanning over three decades. Since the 1990s, he has led security initiatives across high-stakes sectors, including Finance, Telecommunications, Media, and Energy. Professional qualifications over the years have included CISSP, ISO27000 Auditor, ITIL and technologies such as Networking, Operating Systems, PKI, Firewalls. For more information including independent citations and credentials, visit our About page.
Contact:
Editorial Standards
This article adheres to Hackerstorm.com's commitment to accuracy, independence, and transparency:
- Fact-Checking: All statistics and claims are verified against primary sources and authoritative reports
- Source Transparency: Original research sources and citations are provided in the References section below
- No Conflicts of Interest: This analysis is independent and not sponsored by any vendor or organization
- Corrections Policy: We correct errors promptly and transparently. Report inaccuracies to
This email address is being protected from spambots. You need JavaScript enabled to view it.
Editorial Policy: Ethics, Non-Bias, Fact Checking and Corrections
Learn More: About Hackerstorm.com | FAQs
Media Contact
Hackerstorm Press Office
Website: https://www.hackerstorm.com
Data feeds: https://www.hackerstorm.com/search-insights/cisa-kev-cve-data